A more specific
entry-point account.
DebugBear now says its DNS records were compromised through its domain registrar. Additional public records document PredictFolio’s hiring, product announcements and business cohosting.
The vendor points to DNS and its registrar.
In its October 30 update, published at 23:11:16 UTC, DebugBear says its DNS server records were compromised through its domain registrar. It also reports disrupted domain email and says its initial investigation points to a specific customer’s website as the target. This gives a more specific vendor account than its earlier general incident warning. Author binding, publication time and source hashes ↗
The official X syndication and oEmbed responses agree on the account and post. They return a truncated long-post preview; an extra statement about internal systems seen only in a mirror is excluded. We have not independently reconstructed the unauthorized DNS change, its credentials or historical DNS destination.
Current registrar: NameCheap. Its role needs care.
The current Verisign registry response for debugbear.com lists NameCheap, Inc., IANA 1068 as registrar. It lists Cloudflare nameservers and a domain-level last-changed timestamp of October 29, 16:45:50 UTC. Selected registry fields ↗
DebugBear’s statement does not name the registrar. Today’s registry record does not establish which account or system was compromised, what changed at that timestamp, or whether Namecheap’s systems were breached. It supplies corporate infrastructure context, not attacker identity.
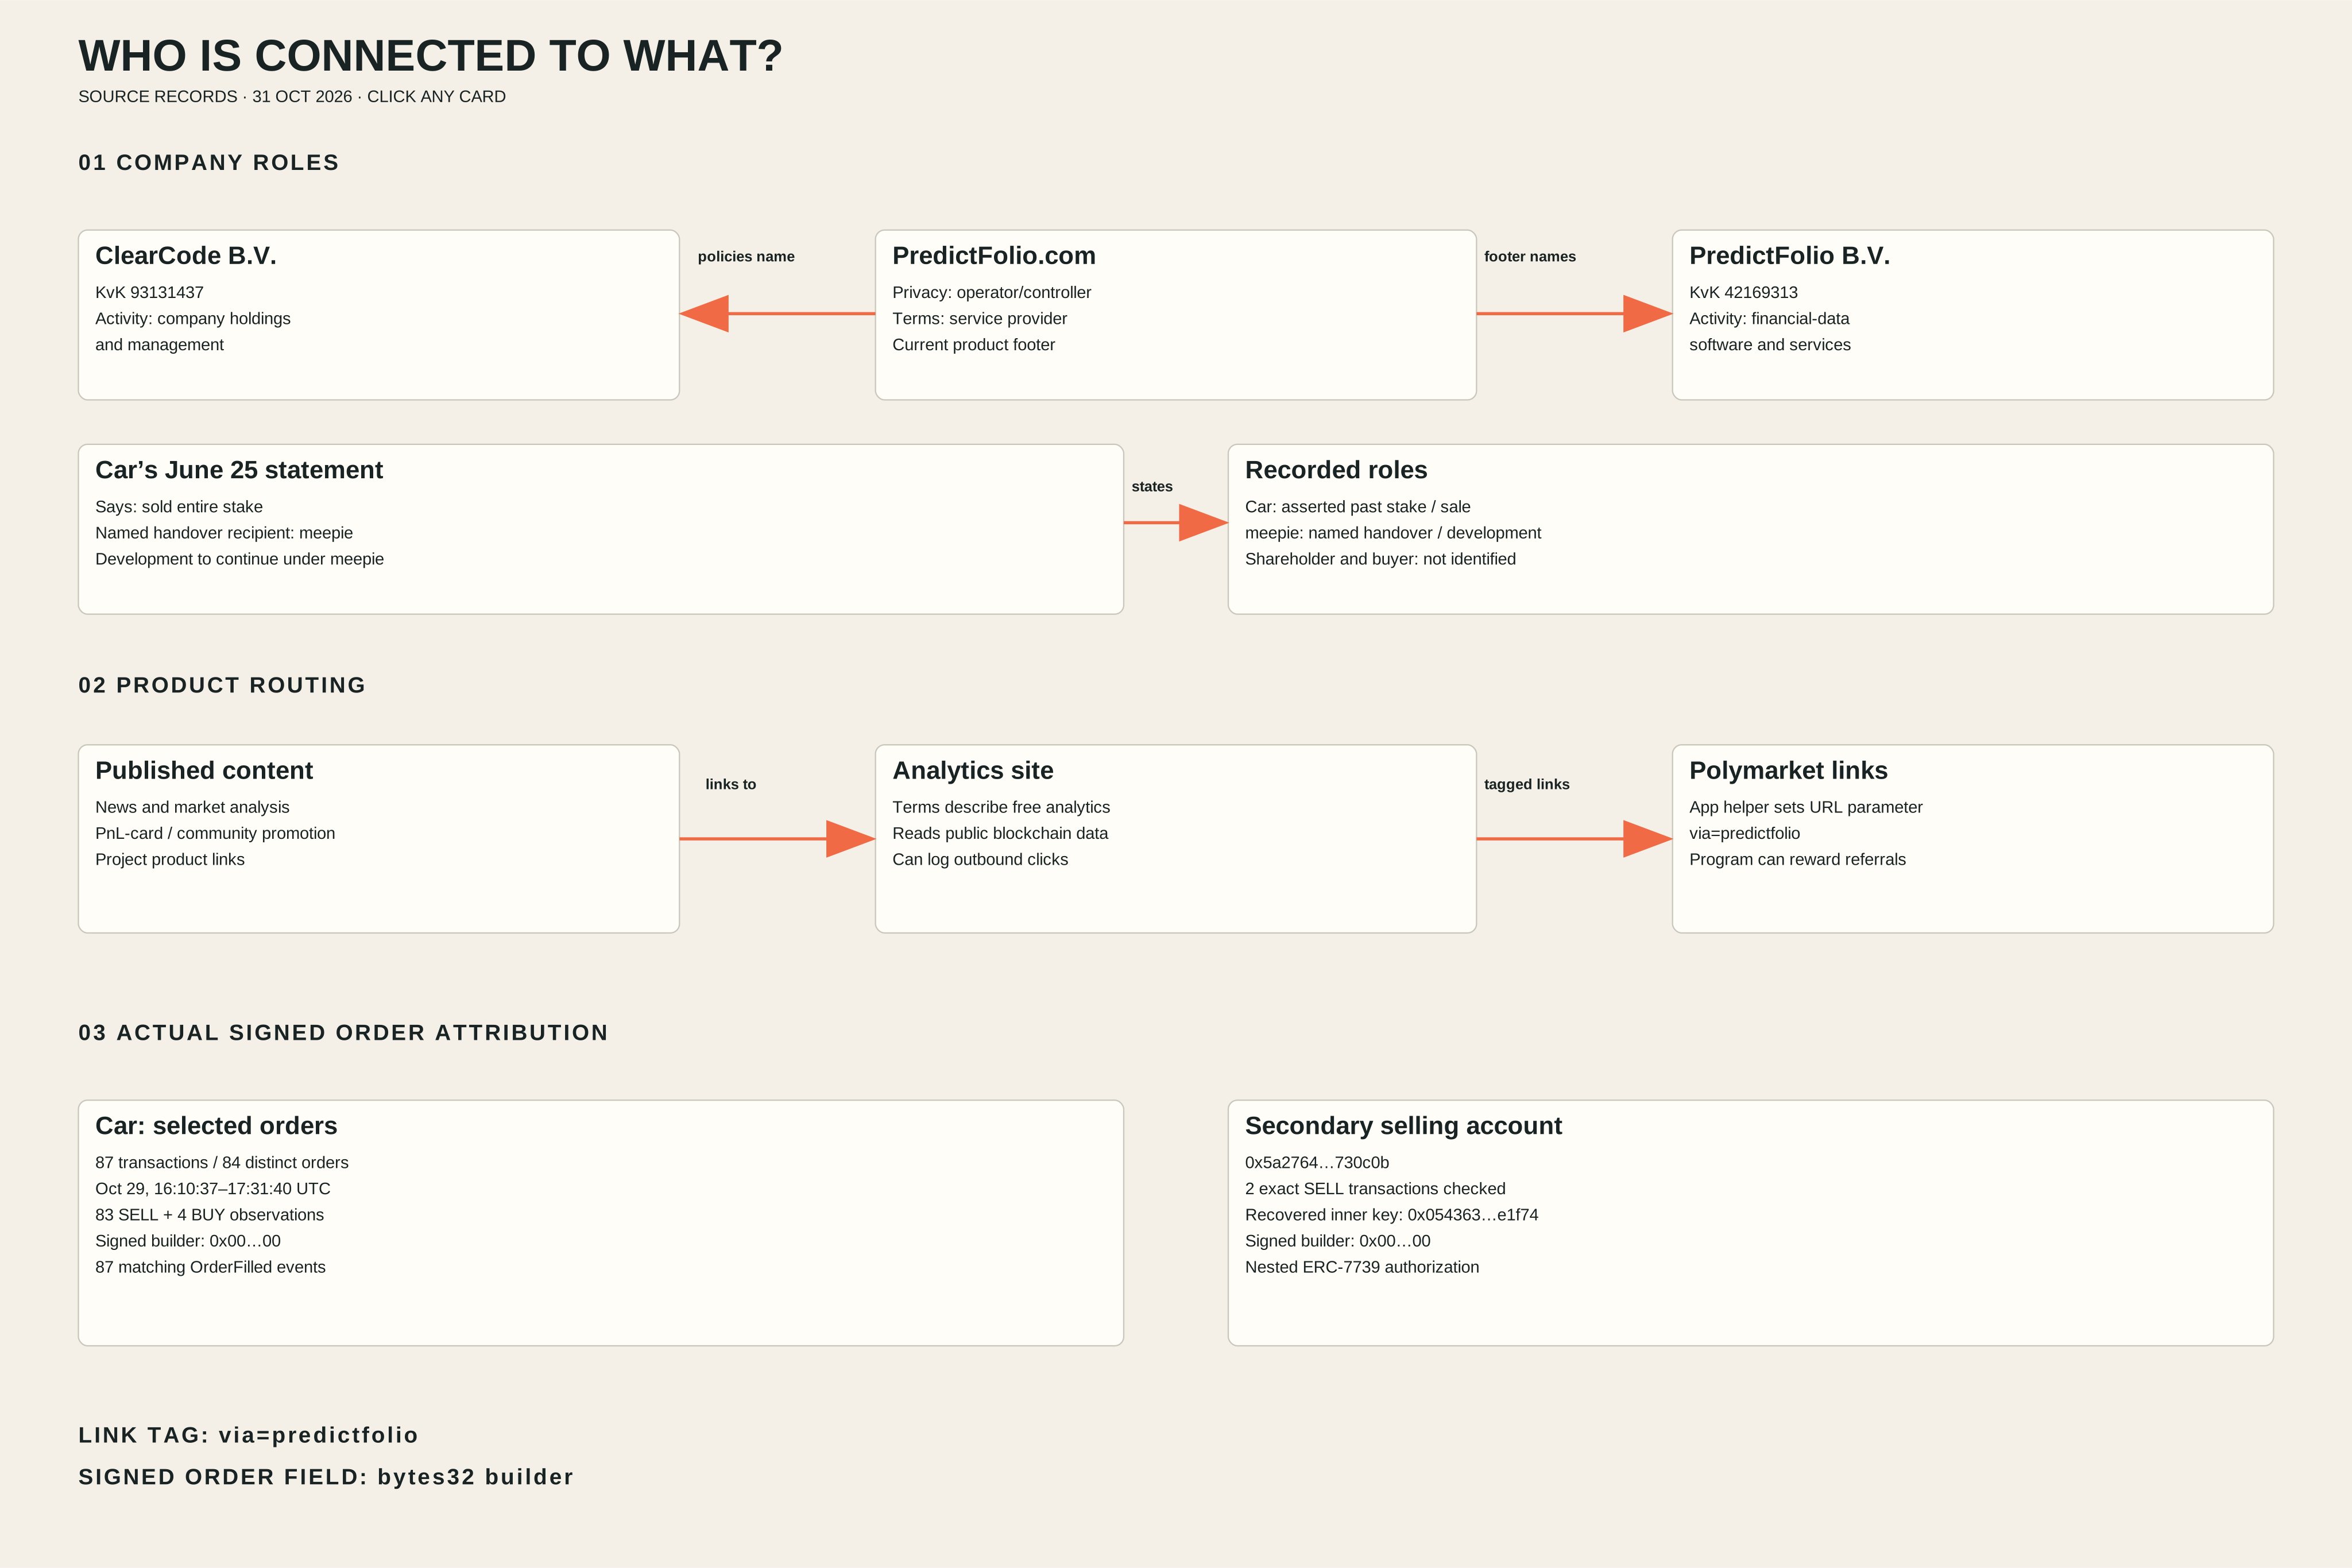
More records of the business after the handover statement.
On August 19, 11:34:09 UTC, an author-bound meepie post advertised Chief Growth Officer and social-media roles for PredictFolio. This independently supports a published hiring role. Its long-post preview supplies no verified revenue figure.
A Luma listing for the October 8 event names PredictFolio and Lattica Finance as business cohosts and links their business websites. That is an additional source for published business association. It is not a shareholding, funding or payment record.
The project’s August 17 announcement describes TradingView Advanced Charts, and another announcement describes tax-report exports. These remain the project’s product claims; no independent TradingView agreement or actual paid sale was recovered. Business-source ledger and limits ↗
The earlier June statement is now recovered directly.
The Polymarket Traders account’s June 25 incident post was published at 14:43:18 UTC. It describes malicious frontend code delivered through a third-party vendor. Car’s stake-sale and handover statement followed at 21:02:04 UTC, a publication gap of 6 hours, 18 minutes and 46 seconds.
These timestamps date the posts. They do not date the sale itself or establish why it happened. Car’s retained full note does not mention that incident or a reason for sale. The comparison supplies no buyer, payment, technical-access or common-attacker evidence. Exact chronology and source bindings ↗
What the additional corporate lookup could establish.
KVK’s documented base-company API can return activity-start, current status and industry fields. Both exact company requests were rate-limited with empty responses, so no new company date was retrieved. Its official FAQ also excludes historical mutation and owner/shareholder/director lookup through those APIs. Lookup scope ↗
The ownership chain and any Car–drainer control relationship remain unverified. No new balance snapshot or company financial amount is included here.
Open the new sources.
Download the 18-file evidence pack ↗
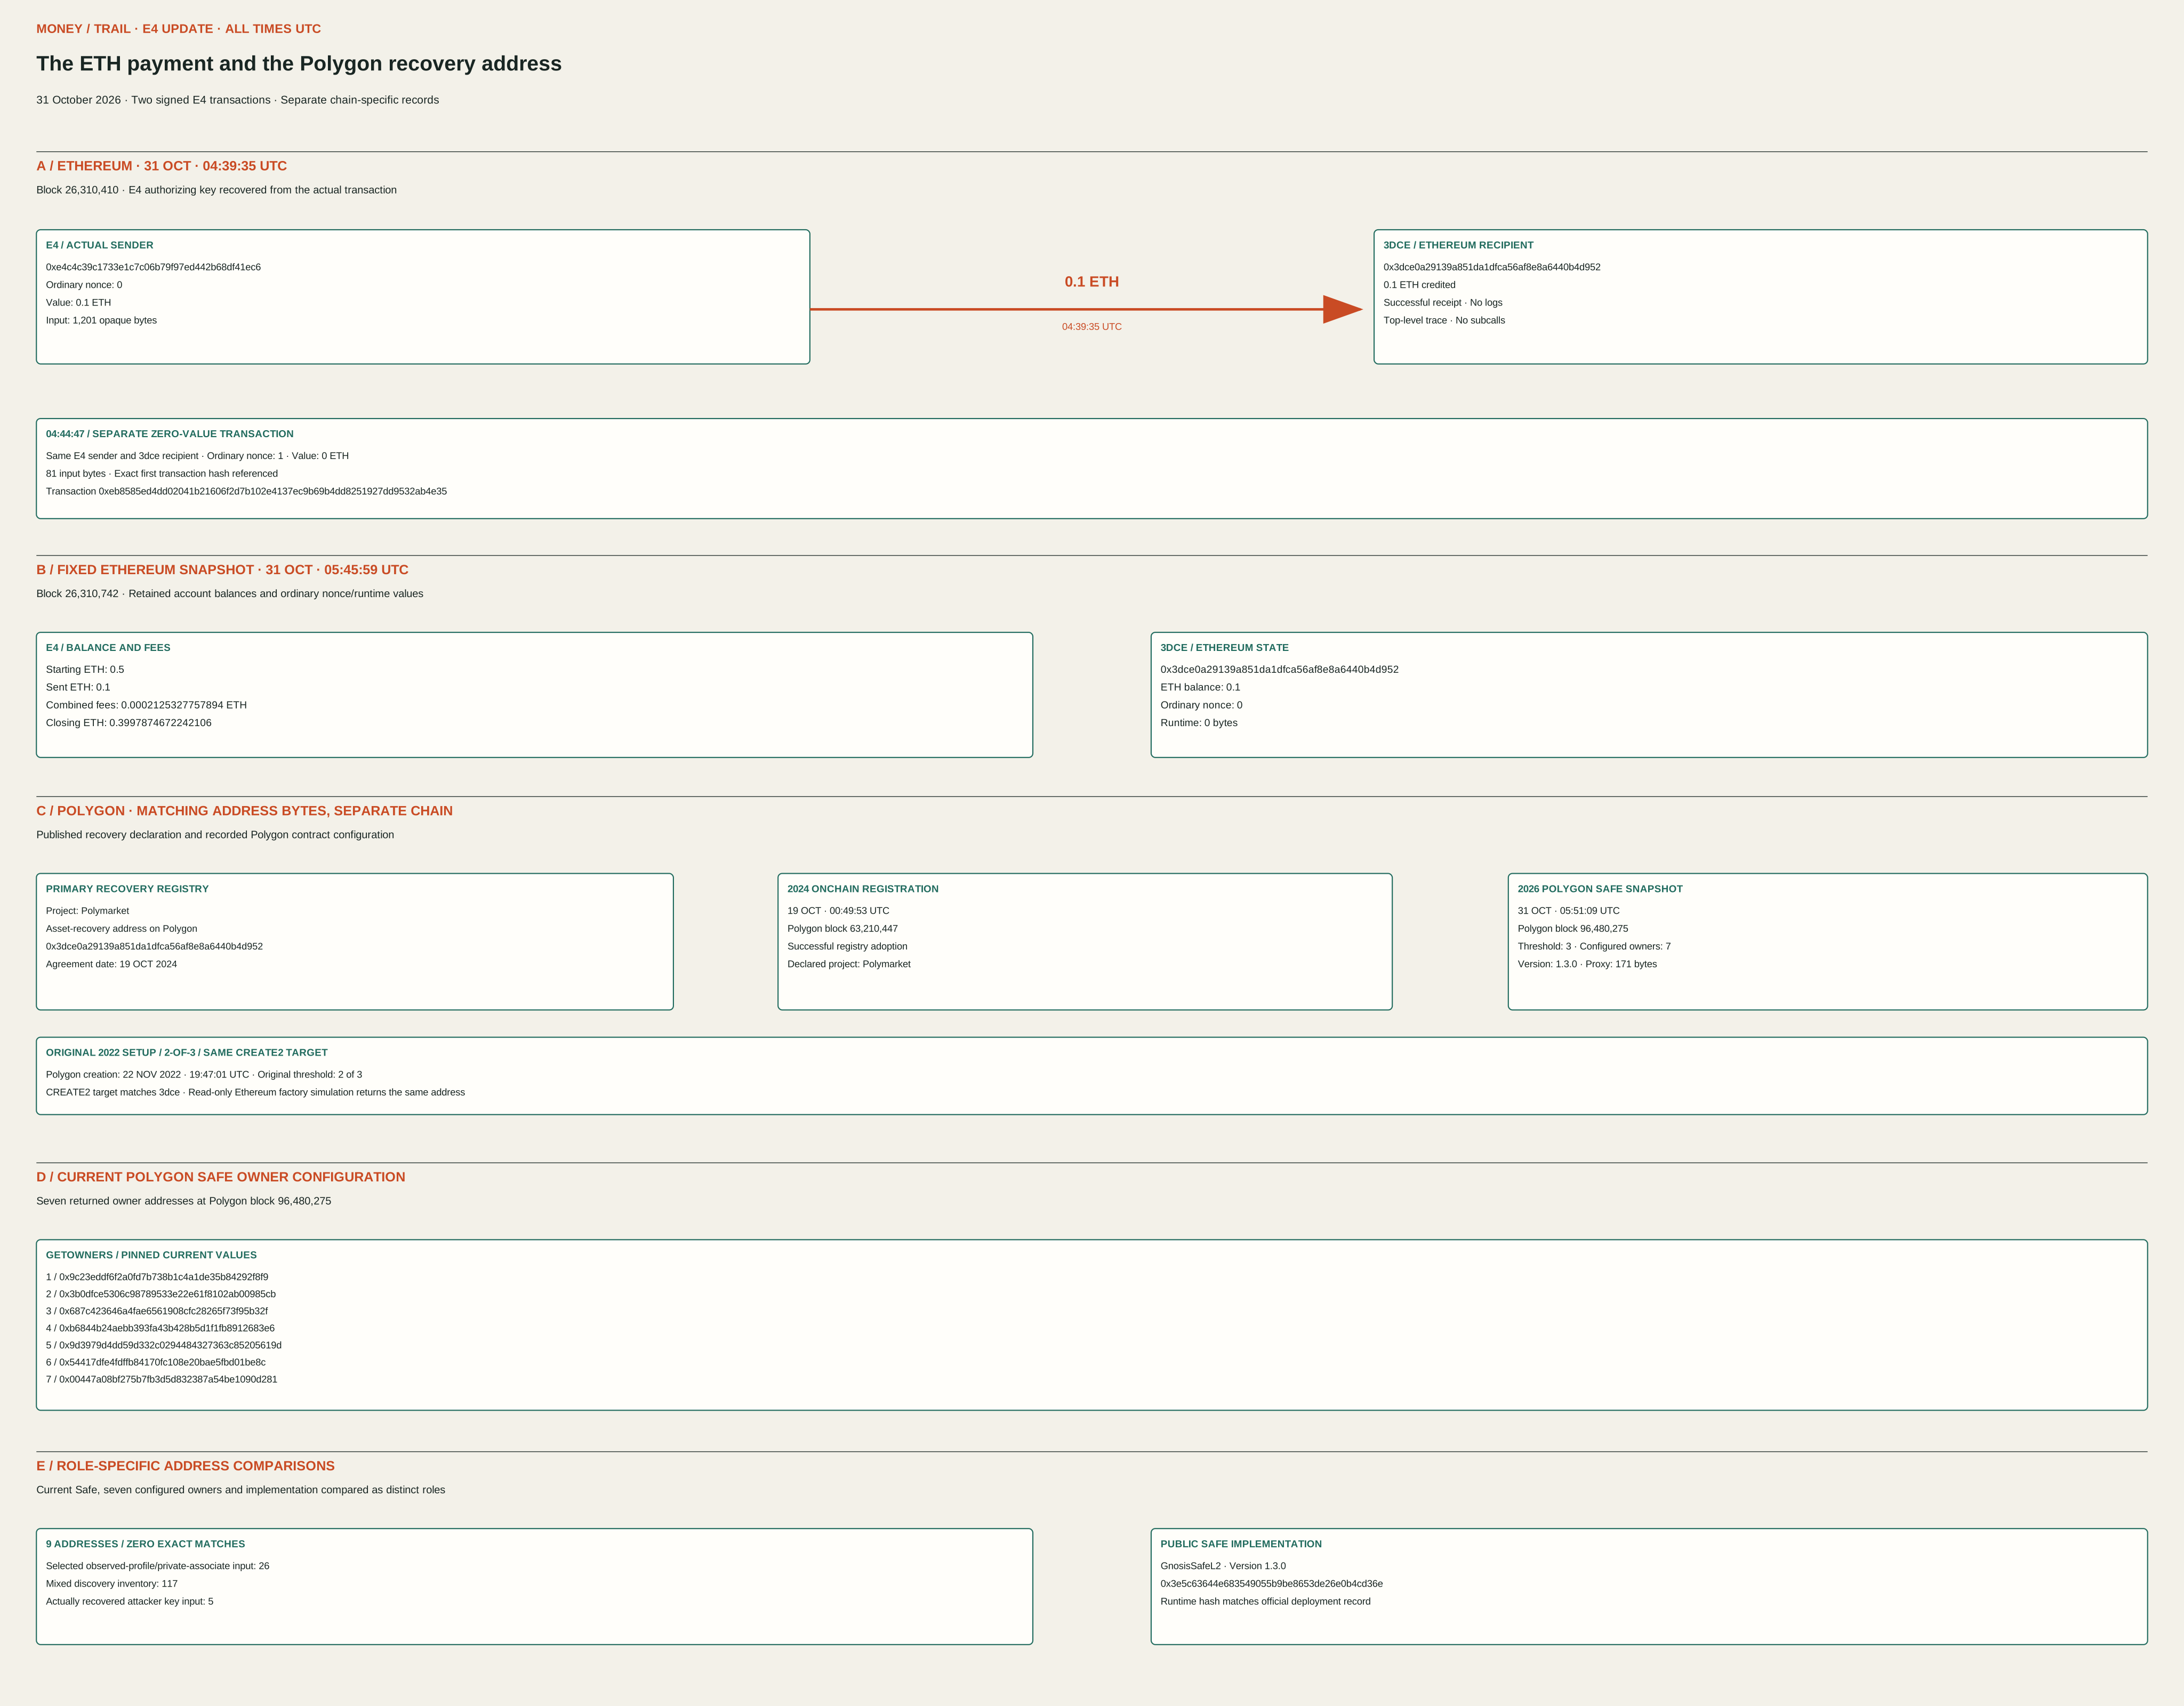
Findings and source scope ↗ · Locations and annual accounts ↗ · Large clickable connections chart ↗ · Dated money chart ↗